
Framework Correlation Automated
Correlate 13 compliance frameworks and 2,791 controls using multi-provider AI with structured rationales. Built for OT/ICS environments where manual mapping takes weeks.
13
Frameworks
2,791
Controls
6-Tier
Confidence
7
OT/ICS Frameworks
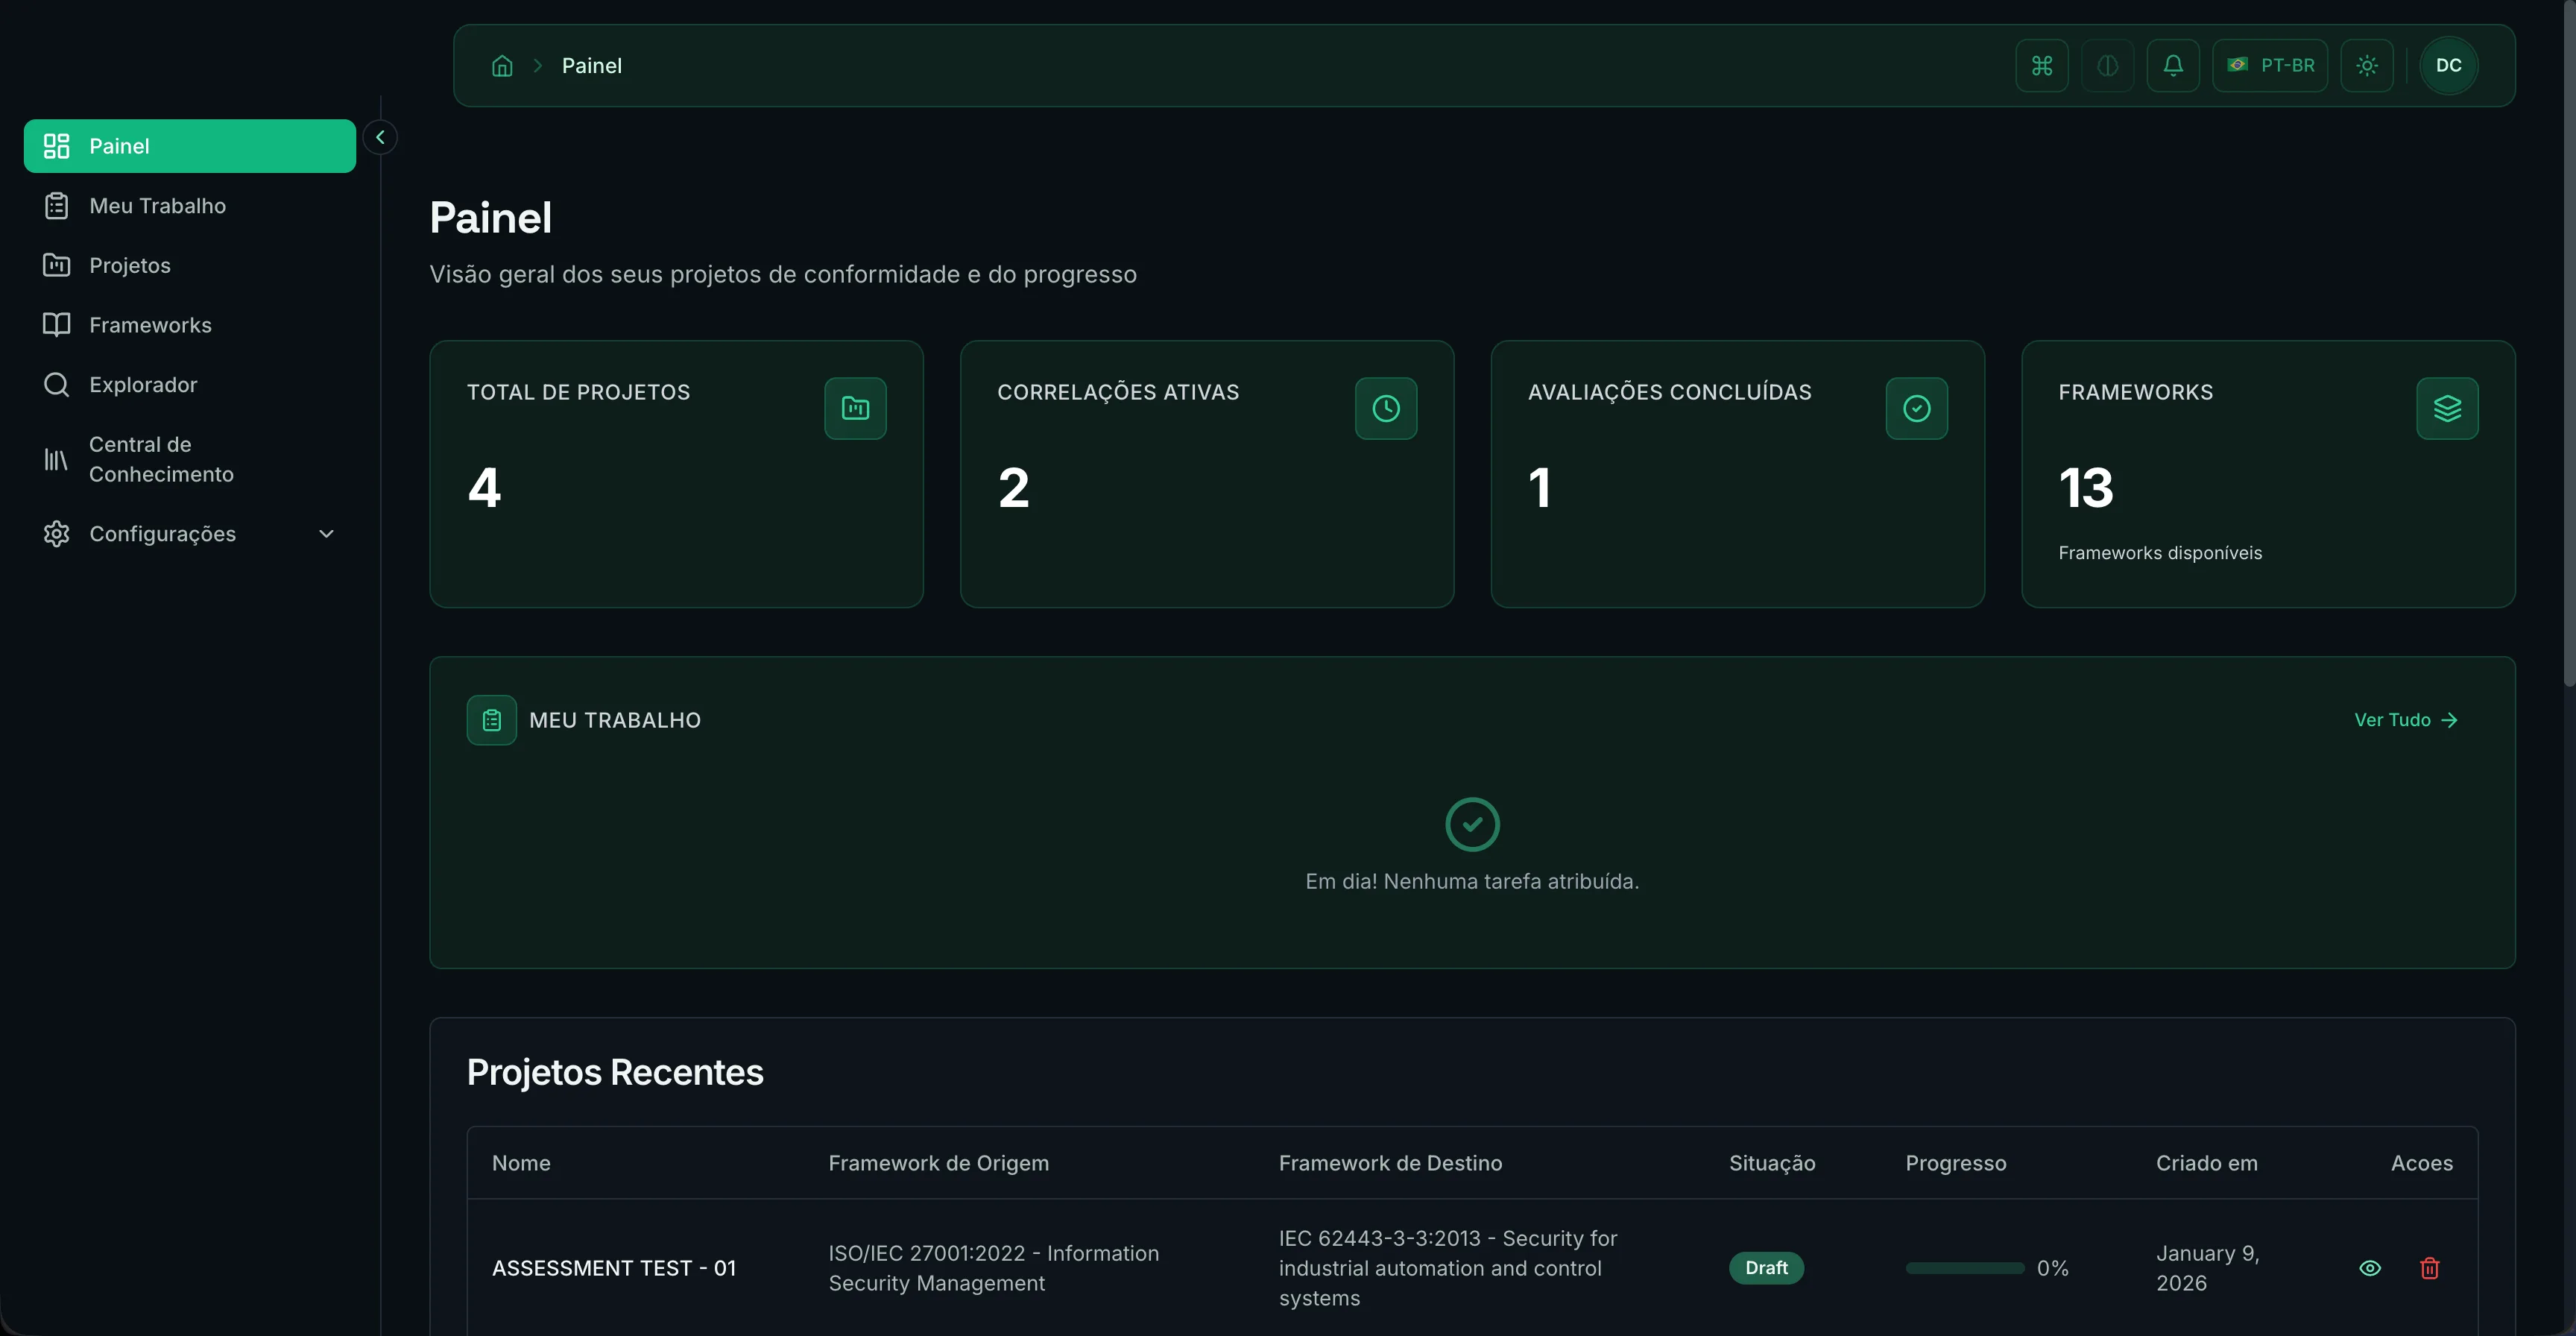
OT/ICS Specialisation
7 of 13 supported frameworks are OT/ICS-specific — IEC 62443, MITRE ATT&CK for ICS, NERC CIP, Saudi OTCC, and more.
- IEC 62443 zone and conduit segmentation modelling
- Security Level (SL 1-4) badges per control
- Industrial protocol awareness: Modbus, DNP3, OPC UA
AI With Transparency
Multi-provider AI (Anthropic Claude, OpenAI, LiteLLM) with semantic vector search. Every mapping includes a structured rationale — not a black-box confidence score.
- 6-tier confidence: Exact, Strong, Moderate, Weak, Suggested, Tentative
- Structured rationale explaining WHY each control maps
- RAG system with organisational knowledge base
Automated Correlation
Manual framework mapping is slow, spreadsheet-driven work. FrameworkMapper correlates entire framework pairs automatically, with a rationale for every mapping.
- Async processing: correlate full framework pairs in minutes
- Evidence reuse suggestions for similar controls
- Implementation roadmap auto-generated from confidence scores
13 Frameworks, 2,791 Controls
The broadest OT/ICS compliance framework coverage available. Correlate across industrial security, IT security, cloud, and regulatory standards in a single platform.
OT/ICS Security (5 Frameworks)
IEC 62443-3-3
Industrial Security
174 controls
MITRE ATT&CK for ICS
OT Threat Intelligence
83 controls
NERC CIP v5-8
Energy Sector
62 controls
Saudi OTCC (OTCC-1:2022)
Middle East OT
180 controls
CISA Catalog v7
Critical Infrastructure
250 controls
IT Security (5 Frameworks)
NIST 800-53 Rev. 5
Federal IT Security
1,189 controls
NIST CSF 2.0
Cybersecurity Framework
106 controls
ISO 27001:2022
Information Security
93 controls
CIS Controls v8
Critical Security Controls
152 controls
NIST 800-171 Rev. 2
CUI Protection (DoD)
110 controls
Cloud Security (2 Frameworks)
CSA CCM v4
Cloud Security Controls
197 controls
CSA CAIQ v4
Cloud Security Assessment
174 controls
Regulatory (1 Framework)
NIS2 Directive
EU Cybersecurity
21 controls
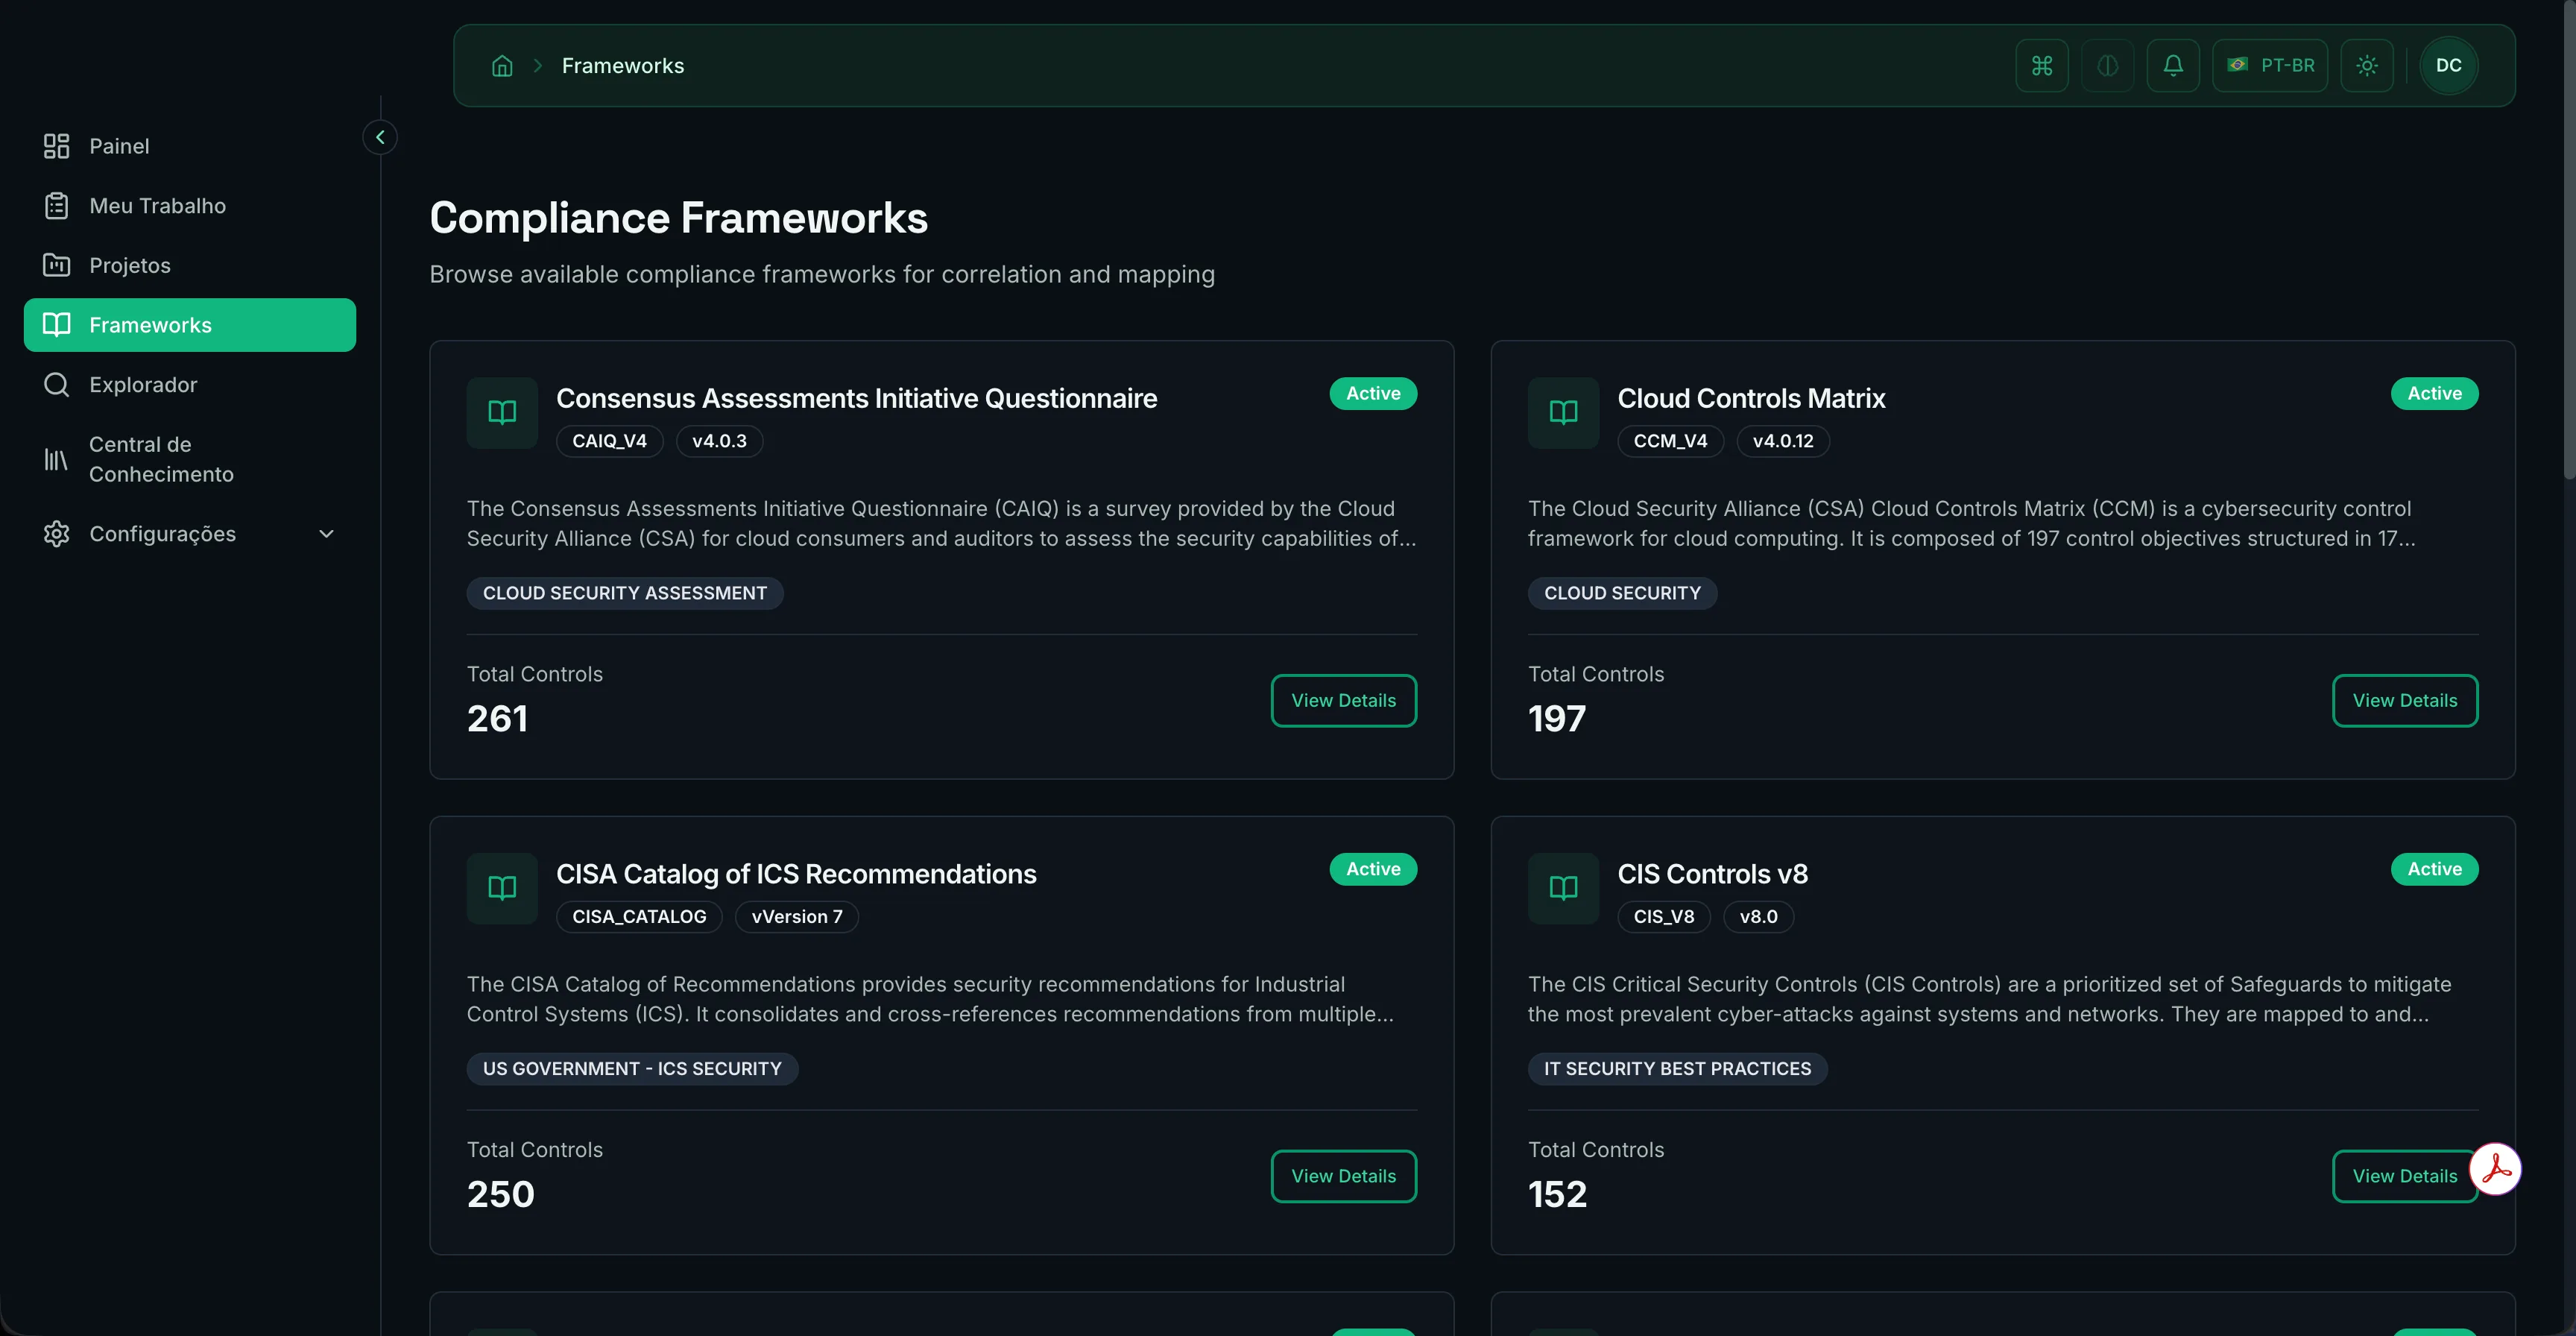
Cloud & IT Security Frameworks
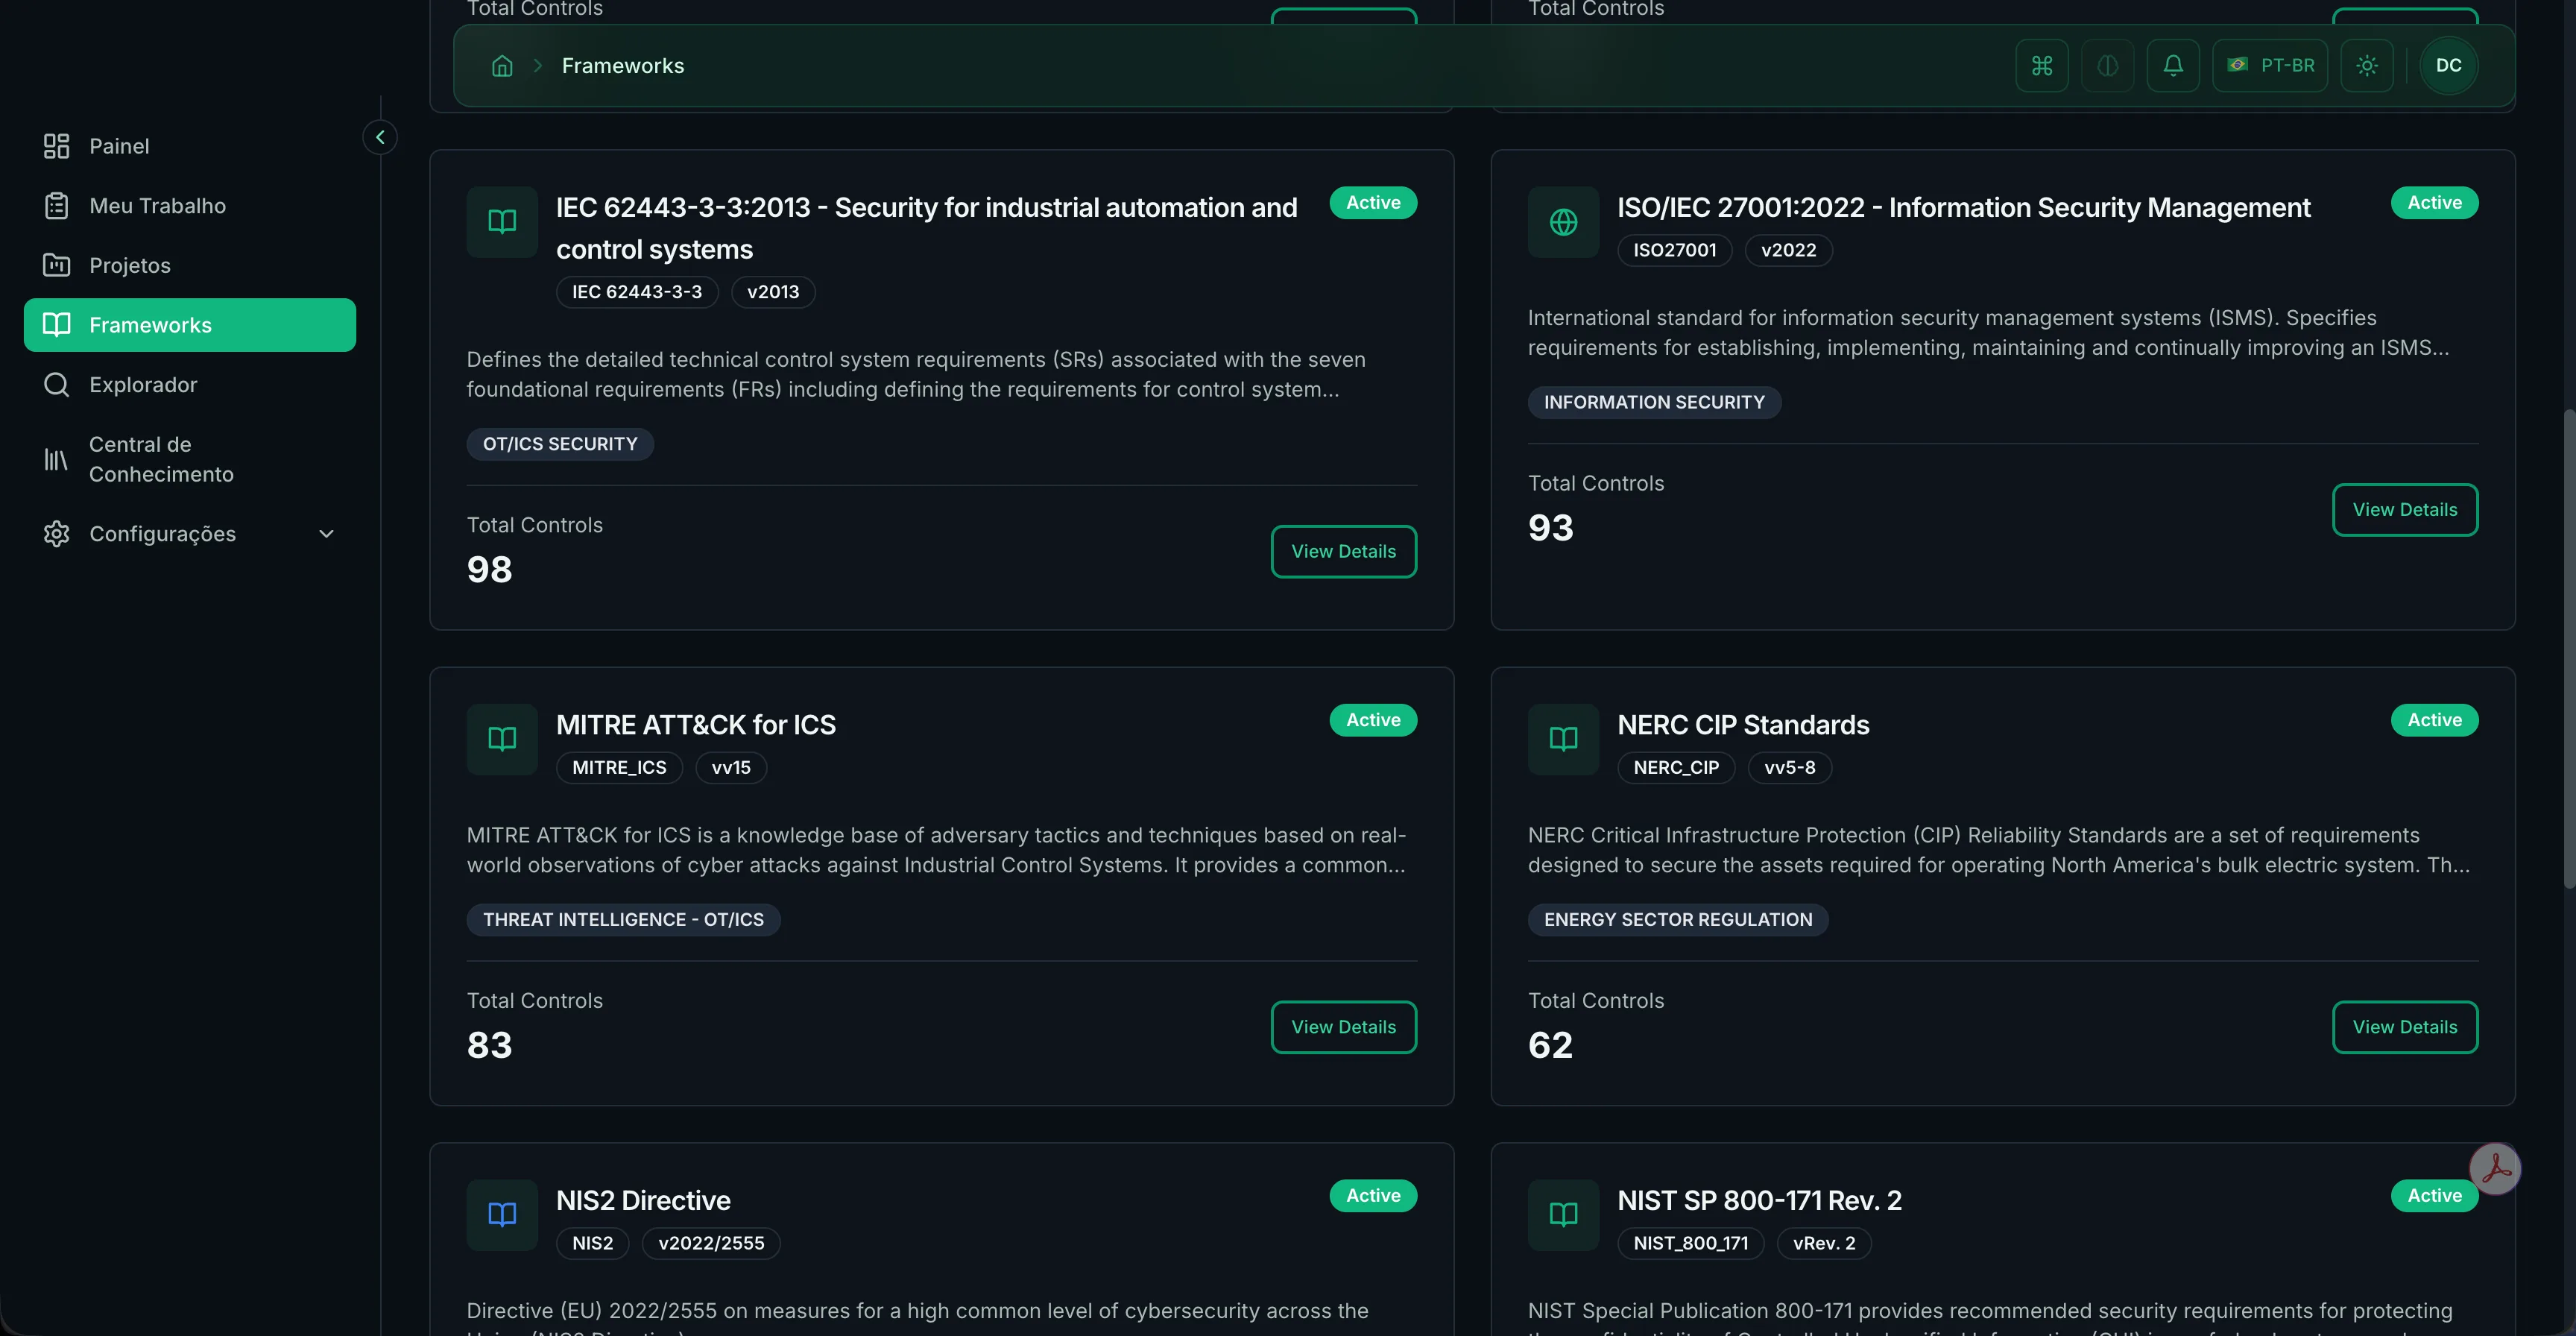
OT/ICS & Information Security
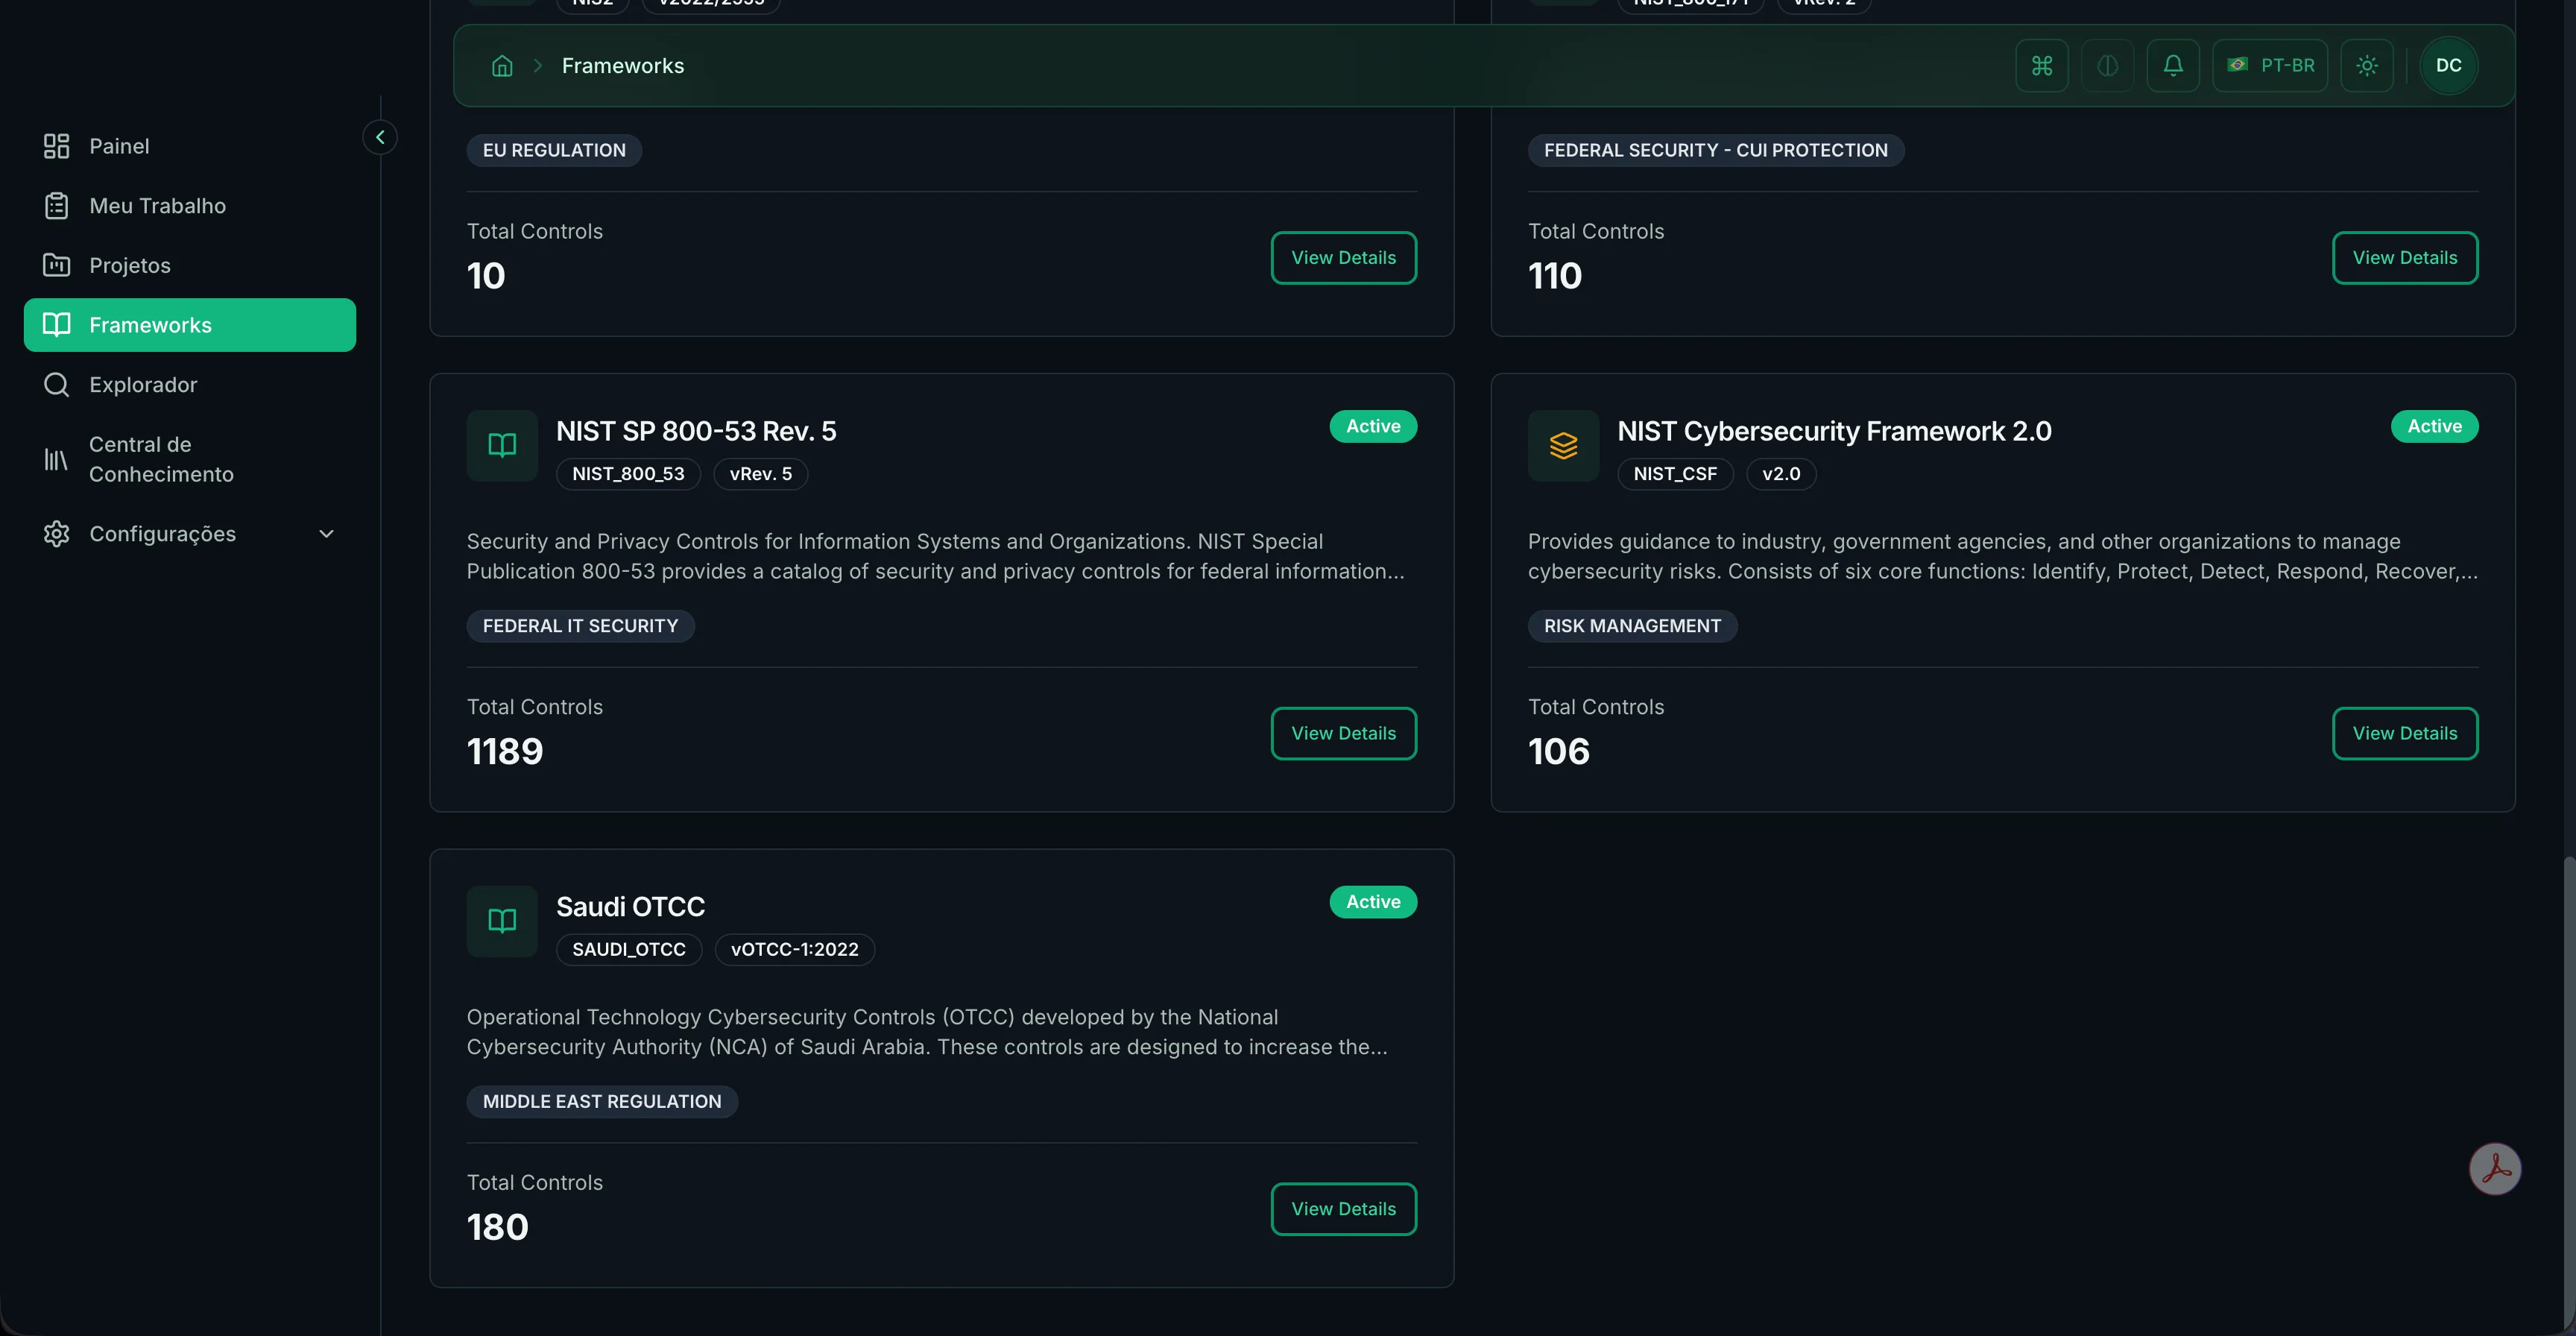
Federal, Regional & Regulatory
AI-Powered Correlation
Multi-Provider AI With Structured Rationales
Semantic vector search using pgvector with HNSW indexing identifies related controls. Multi-provider AI (Anthropic Claude, OpenAI, LiteLLM) generates structured rationales explaining each correlation. Every mapping is auditable.
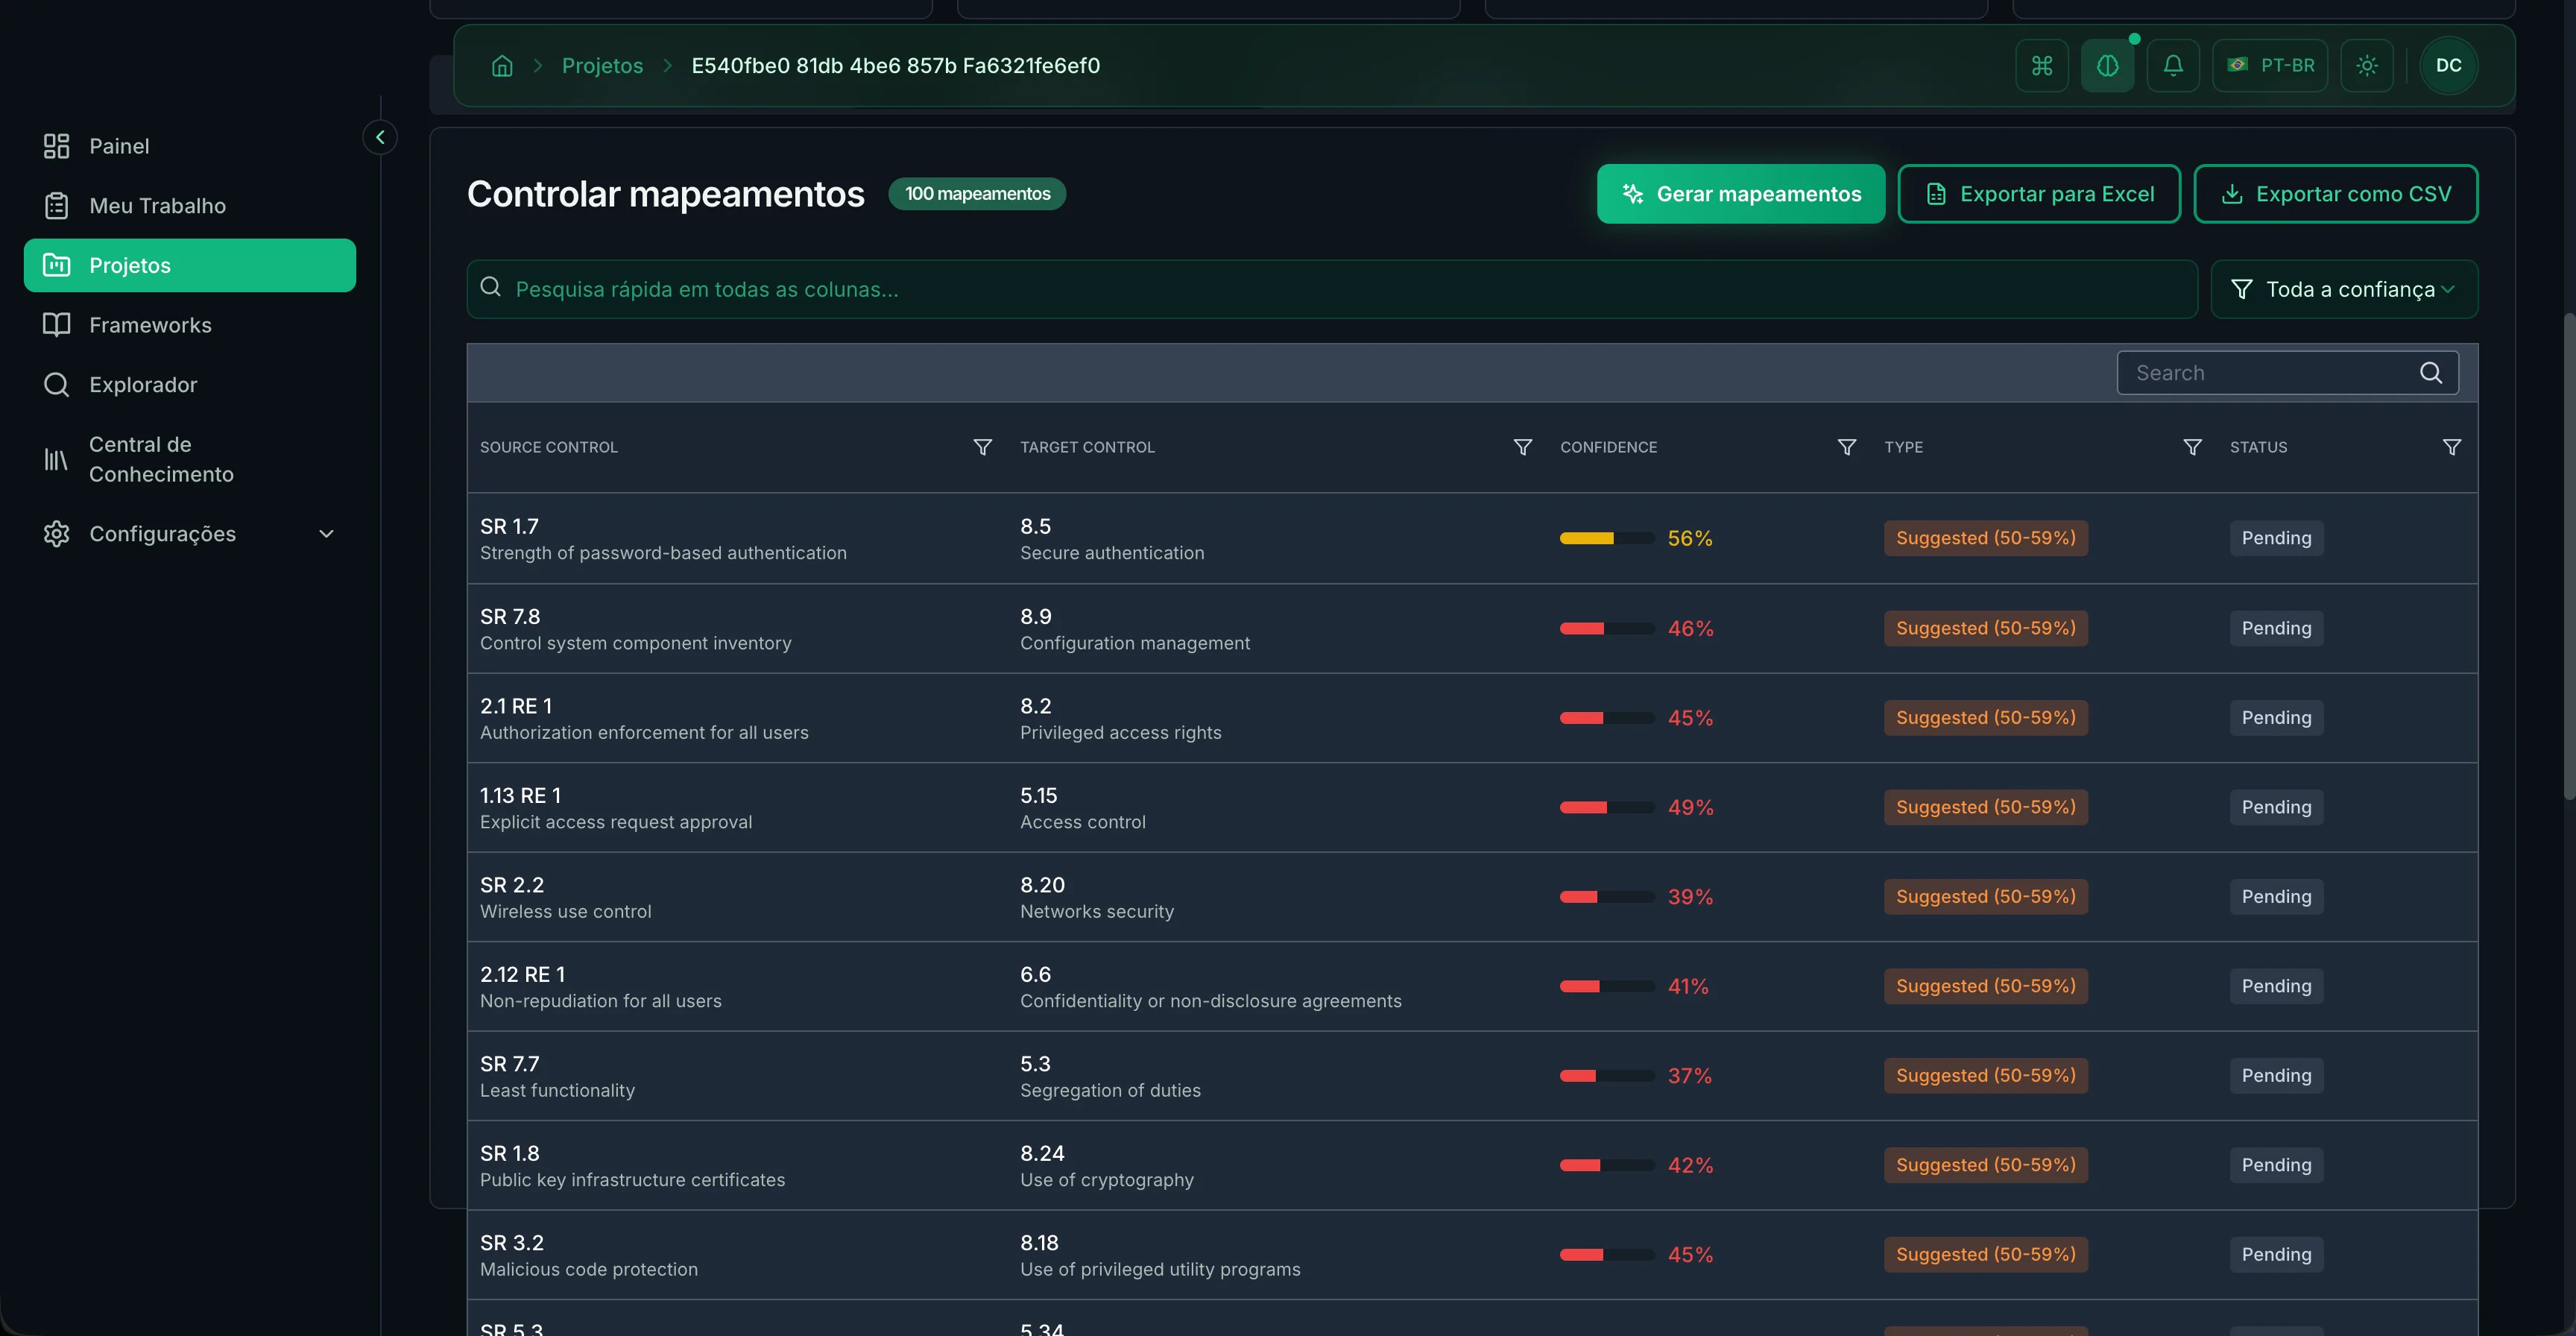
Control-to-Control Mappings
View every mapping with source control, target control, confidence score, type classification, and validation status. Export to Excel or CSV for offline analysis. Generate new mappings or refine existing ones with a single action.
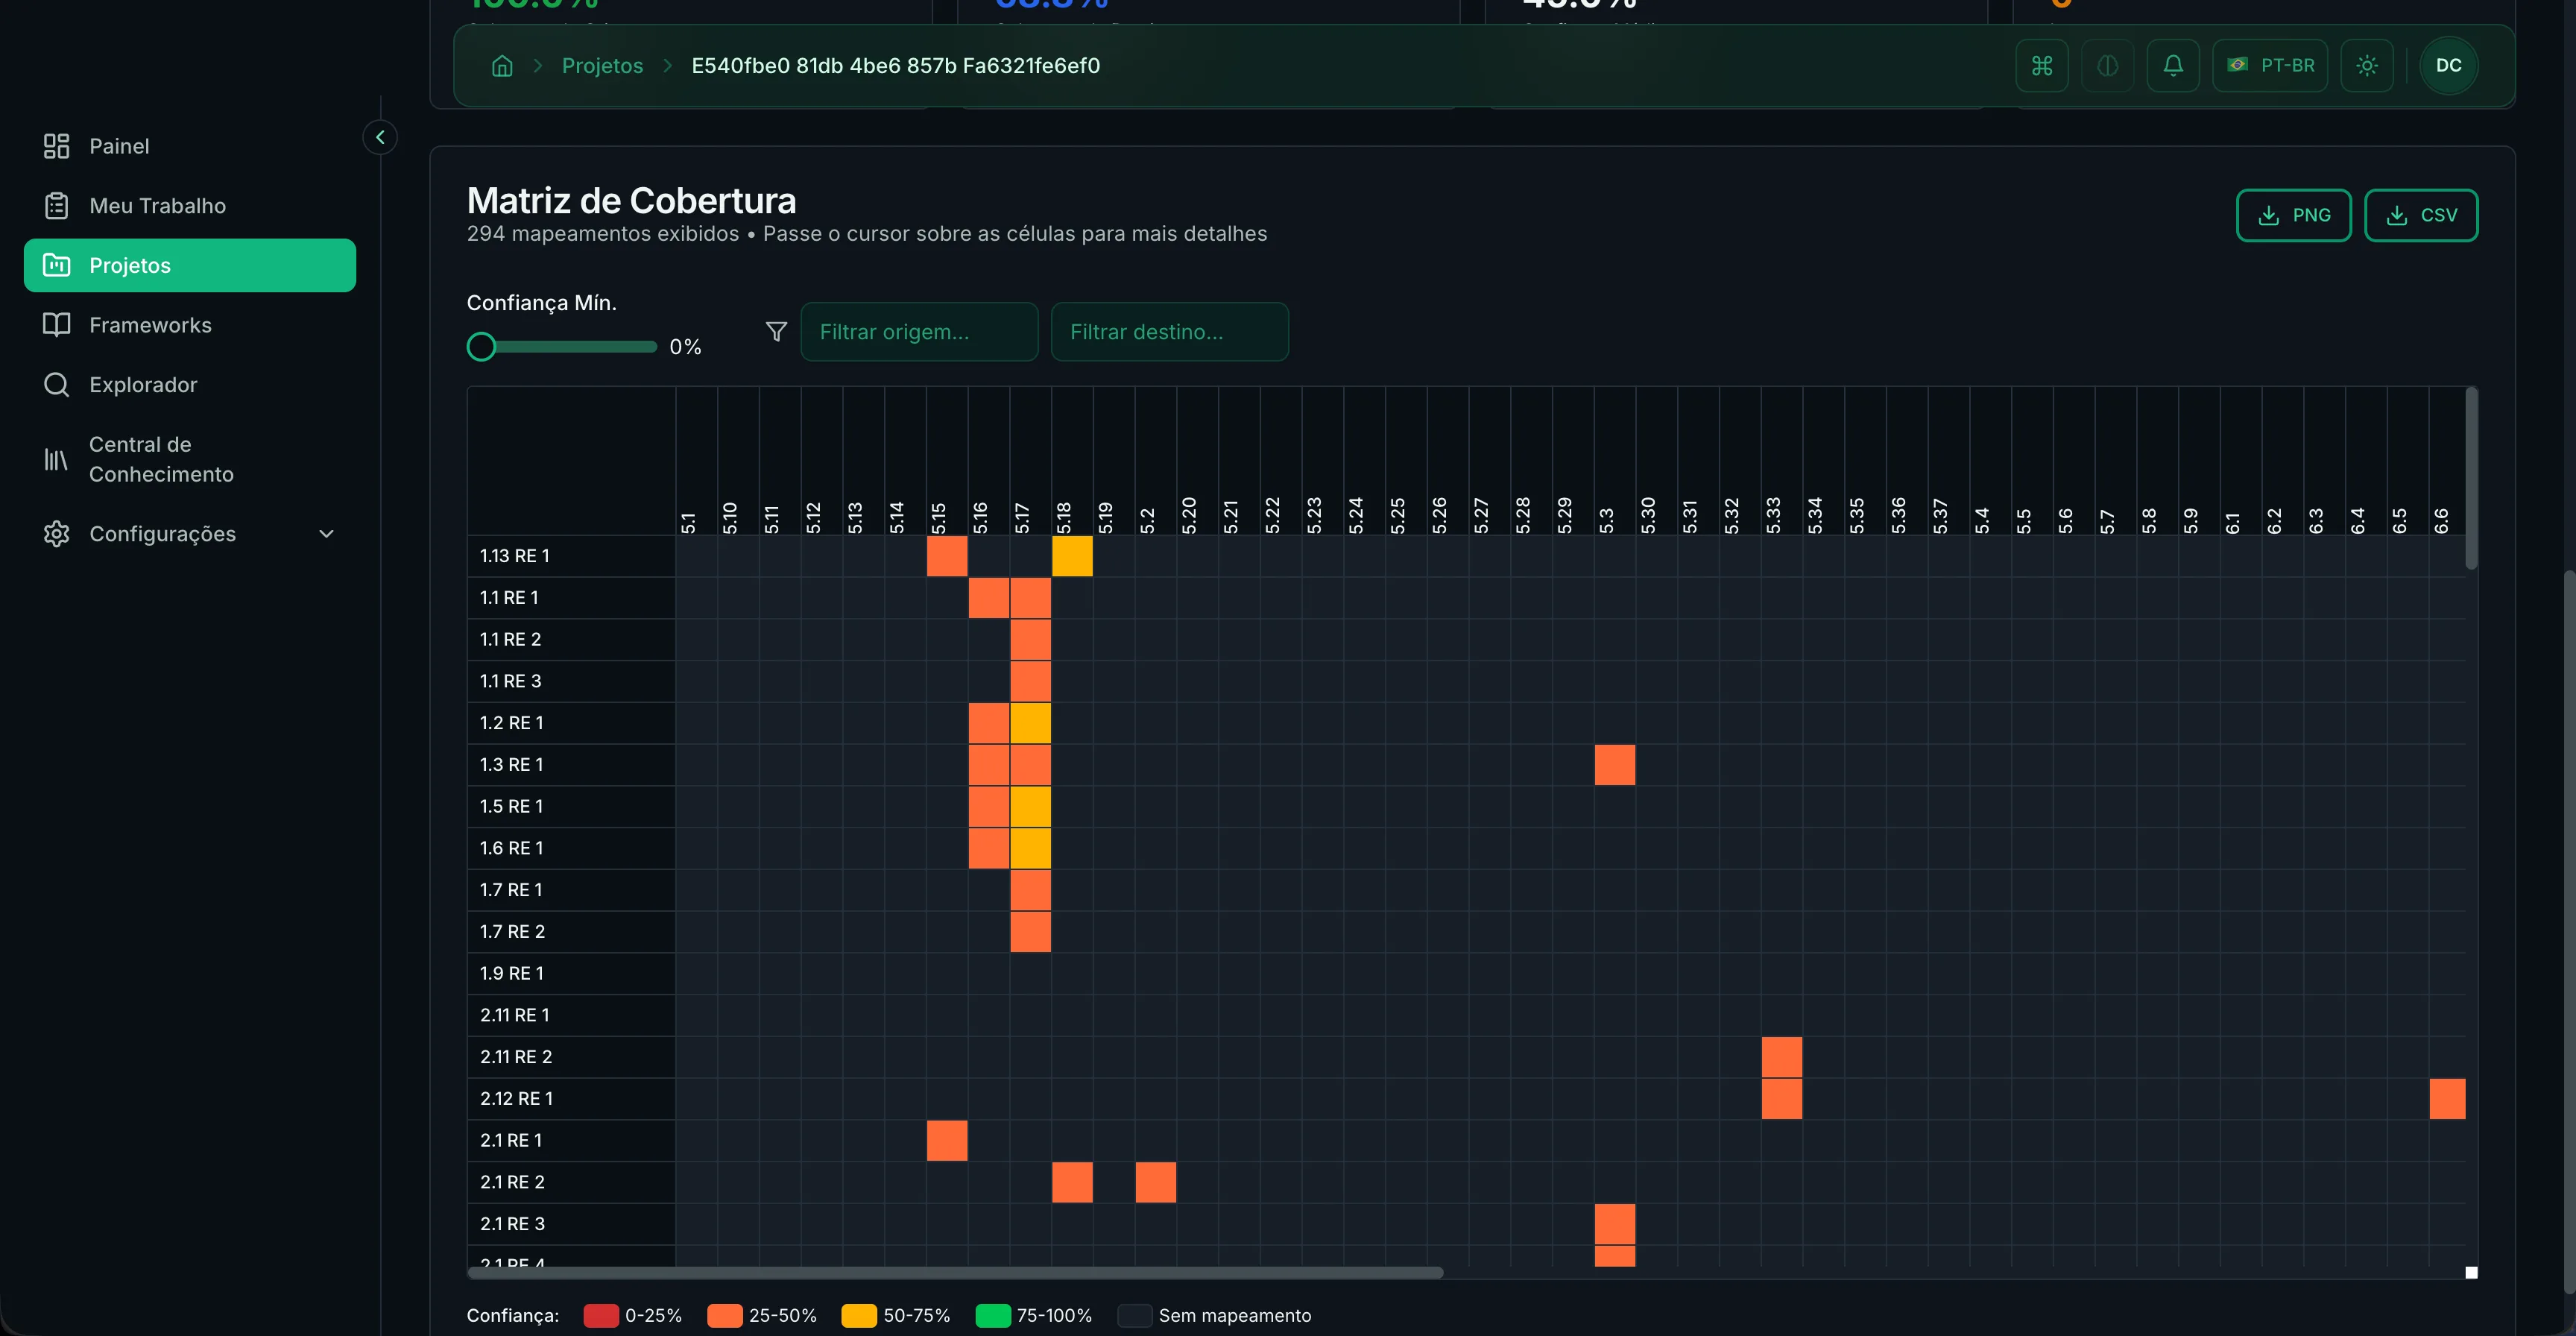
Coverage Matrix — visual heatmap of all mappings
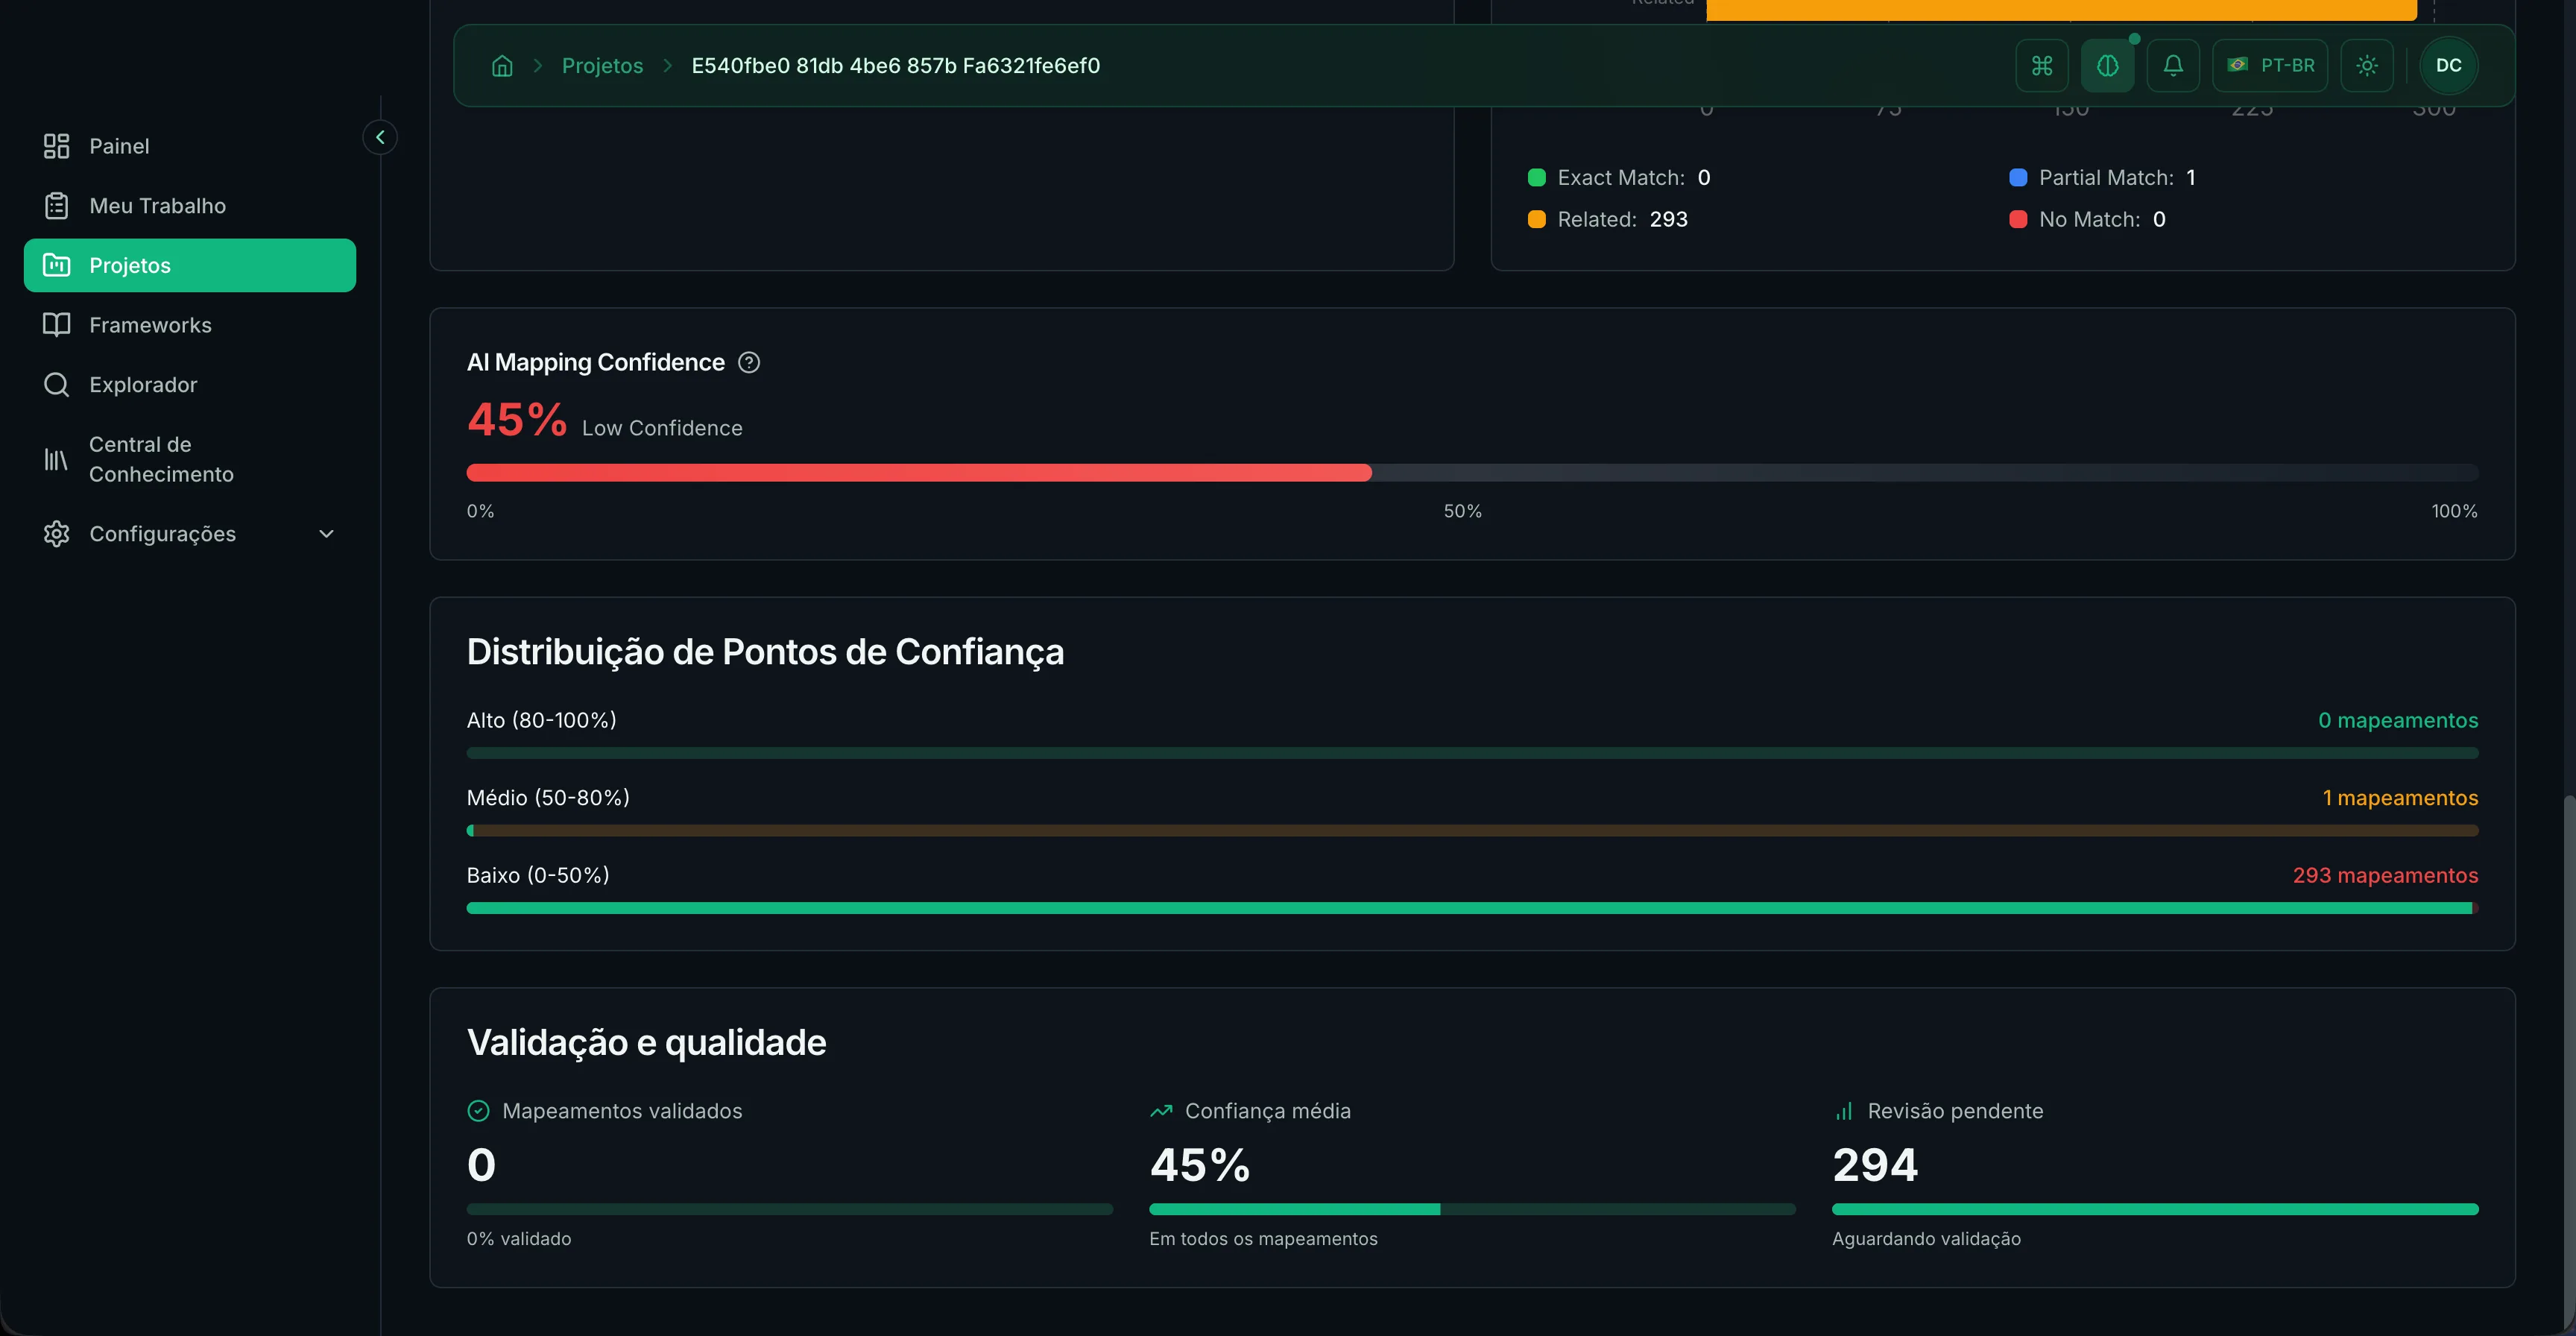
Confidence Distribution — quality metrics at a glance
Evidence, Implementation & Roadmap
Link evidence to specific controls, track implementation status, and generate implementation roadmaps automatically from mapping confidence scores. Reuse evidence across similar controls to eliminate duplicate work.
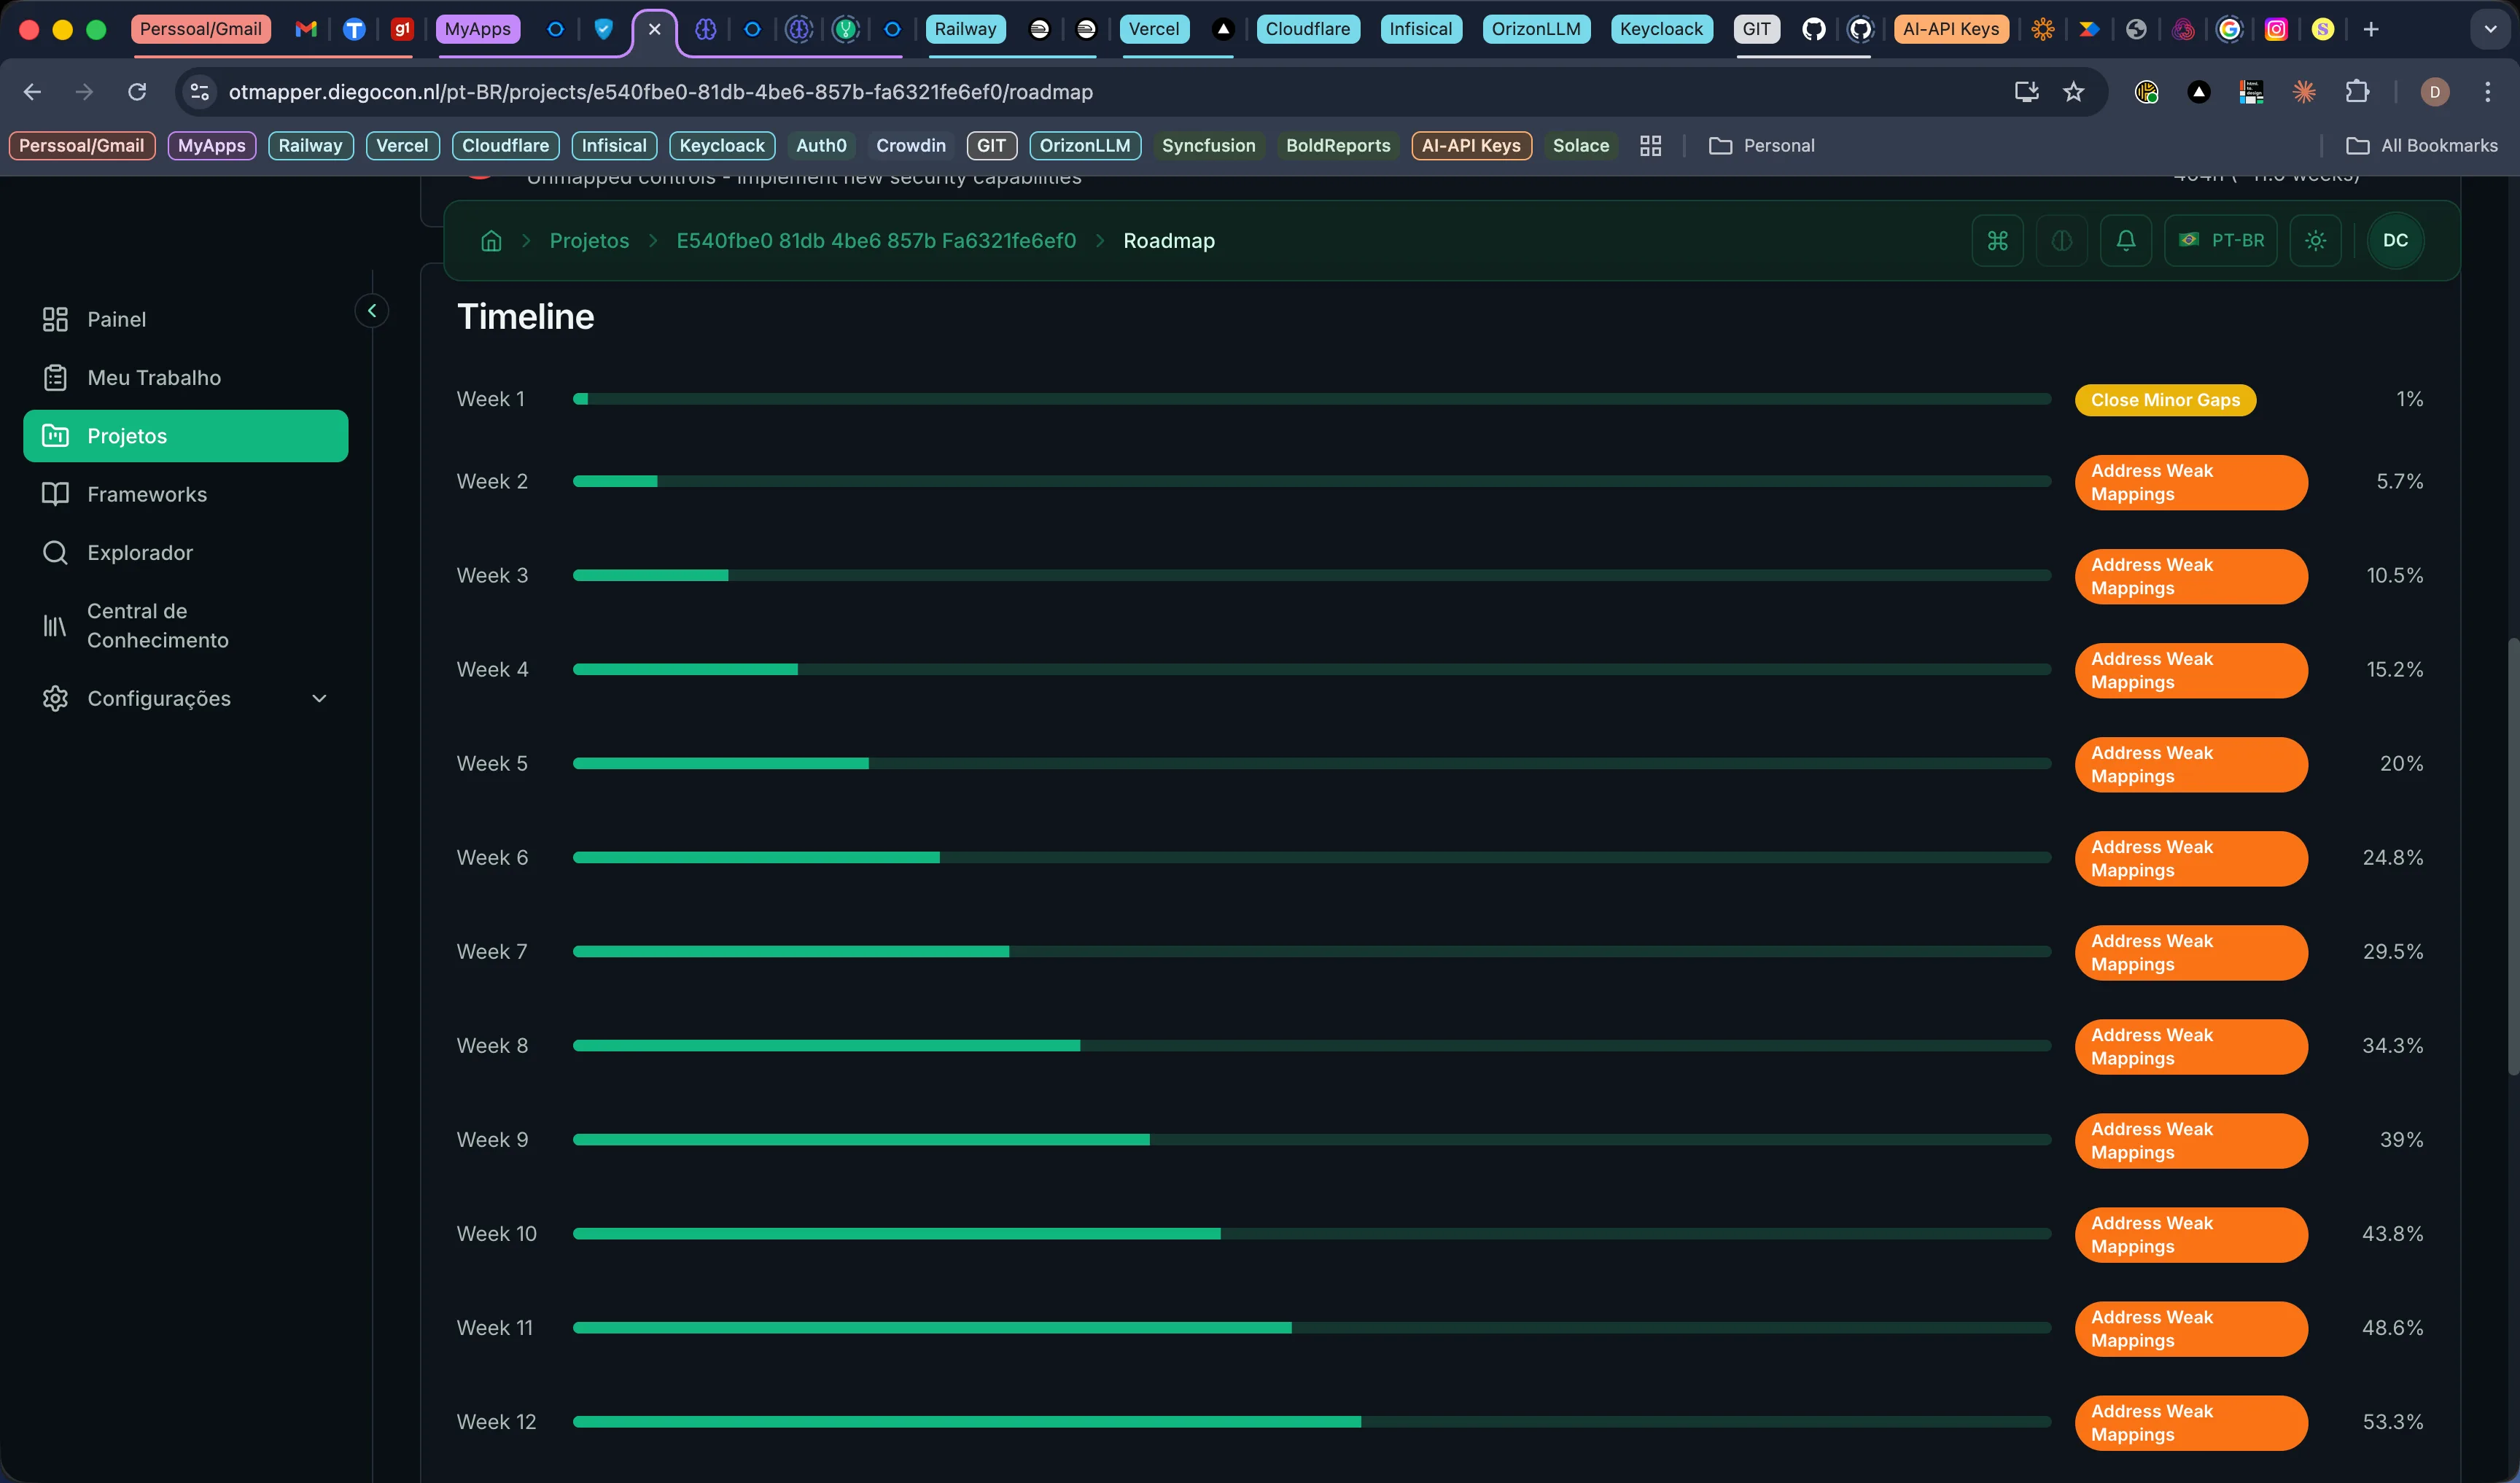
Auto-Generated Roadmap
The platform analyses mapping confidence scores and implementation gaps to generate a week-by-week roadmap. Prioritise minor gaps first to build momentum, then address weak mappings requiring deeper implementation work.
- Implementation status per control: Not Started, In Progress, Implemented, Not Applicable
- Team size and hours-per-week configuration for effort estimates
- Reminder system for compliance deadlines
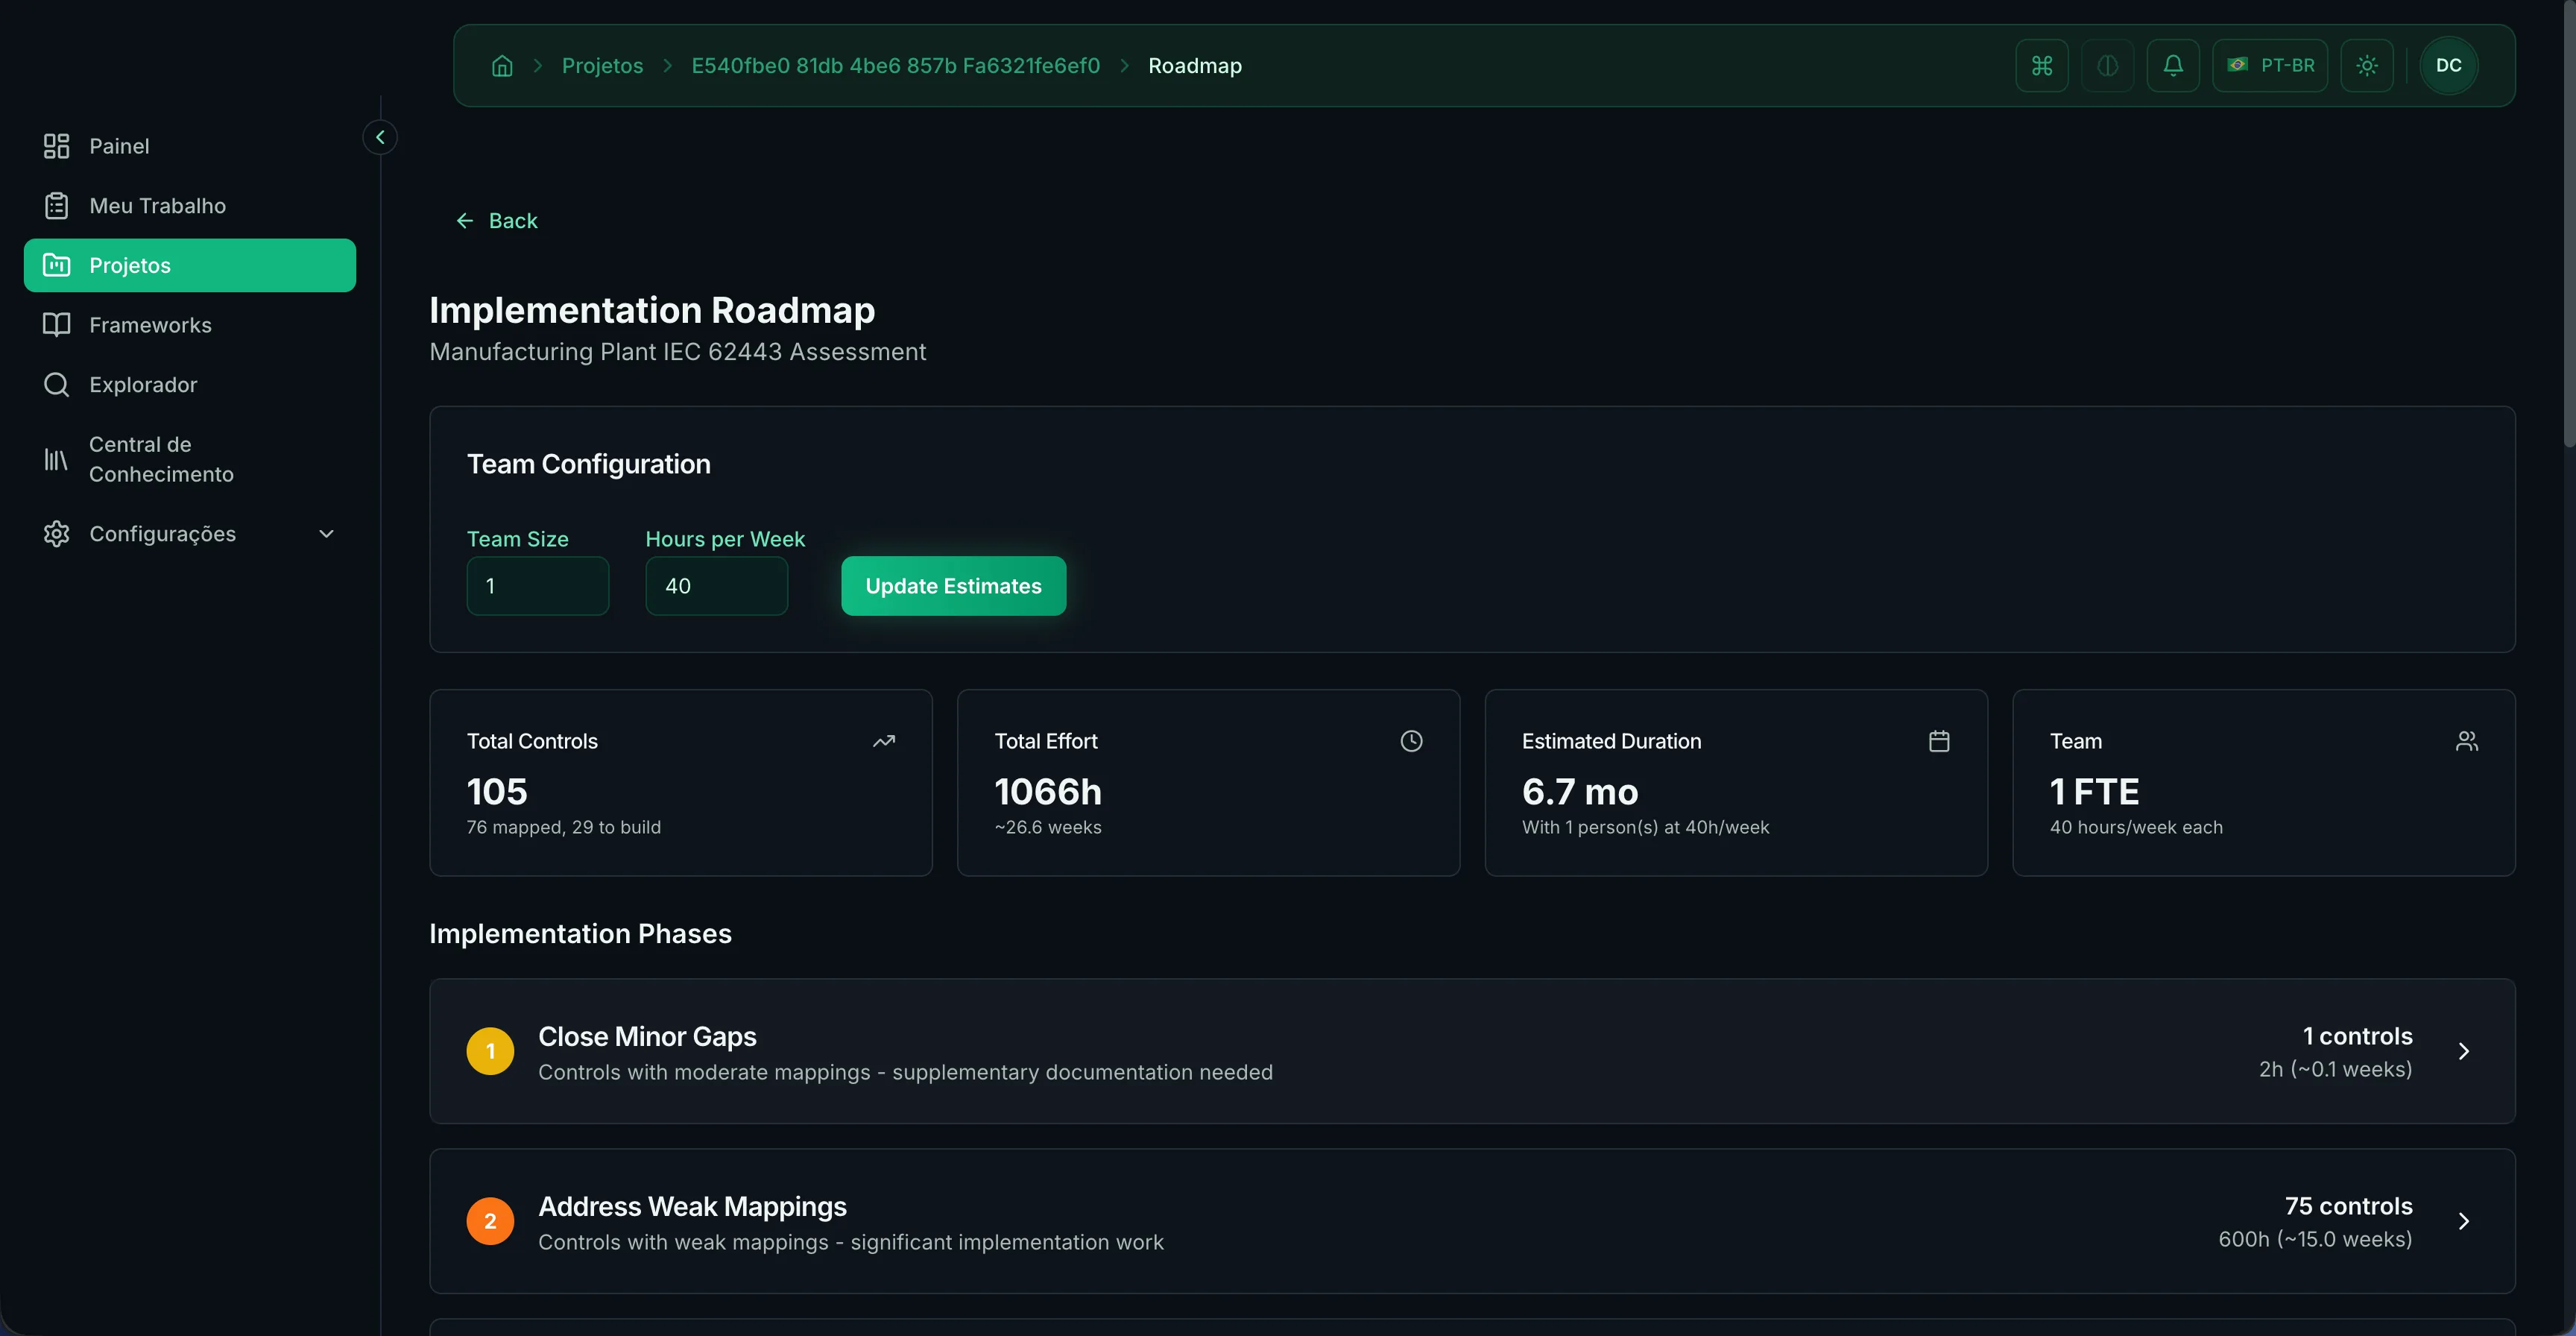
Effort Estimation
Configure your team size and available hours to get realistic duration estimates. The platform breaks implementation into prioritised phases — close minor gaps first, then address controls with weak mappings that require more work.
Evidence reuse across similar controls
When a control maps to multiple frameworks, upload evidence once and link it everywhere. The platform suggests reuse opportunities automatically.
4 Professional PDF Report Types
Generate board-ready reports directly from your correlation data. Each report type serves a different audience — from executive summaries to detailed control-by-control analysis.
Compliance Summary
Executive scorecard with KPIs, confidence distribution, and overall compliance posture.
Gap Analysis
Unmapped controls, risk assessment, and remediation recommendations prioritised by impact.
Mapping Correlation
Control-by-control mappings with AI rationales, confidence scores, and linked evidence.
Executive Dashboard
High-level compliance status with trend charts for board-level reporting.
Built for Industrial Sectors
Industry-specific framework recommendations through a guided wizard. Select your industry, regulatory requirements, and security goals — the platform recommends the optimal framework pairs to correlate.
Energy & Utilities
NERC CIP + IEC 62443
Bulk electric system compliance with industrial control system security — covering both regulatory obligations and operational technology protection.
Oil & Gas
IEC 62443 + Saudi OTCC
Industrial automation security for upstream, midstream, and downstream operations with regional regulatory coverage for Middle East operations.
Manufacturing
IEC 62443 + CIS Controls
Secure production environments by correlating industrial security standards with IT security best practices across converged IT/OT networks.
Water & Wastewater
CISA Catalog + NIST CSF
Critical infrastructure protection aligned with federal guidance — covering SCADA systems, treatment facilities, and distribution networks.
Defence & Government
NIST 800-53 + NIST 800-171
Federal security controls with CUI protection for defence contractors and government agencies handling sensitive information.
4-question industry wizard — 13 industry options including 10 OT/ICS-specific industries. Rule-based recommendation engine suggests optimal framework pairs with confidence scoring.
Enterprise-Grade Security
Built for organisations that take security seriously. Every feature is designed with multi-tenant isolation, auditability, and enterprise authentication in mind.
Role-Based Access Control
5-level RBAC: Superadmin, Admin, Analyst, Auditor, and Viewer — with granular permissions across all platform resources.
Single Sign-On
Keycloak SSO via OpenID Connect with Microsoft SSO support. Conditional fallback to credential-based authentication.
Multi-Tenant Isolation
Complete organisation isolation with tenant-scoped data access. No cross-tenant data leakage by design.
Encryption & Storage
Field-level encryption for AI provider API keys. S3-compatible encrypted file storage for evidence and reports.
Complete Audit Trail
Every action logged with timestamps, user identity, and IP address. Full traceability for compliance auditors.
API & Integration
API key management for programmatic access with configurable rate limiting. WebSocket real-time notifications with heartbeat monitoring.
See FrameworkMapper in Action
Whether you are mapping two frameworks or building a multi-regulatory compliance programme, FrameworkMapper scales with your needs.